Preview






Description
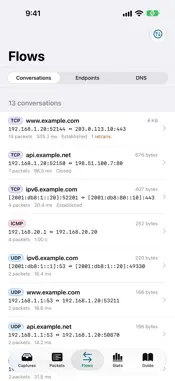
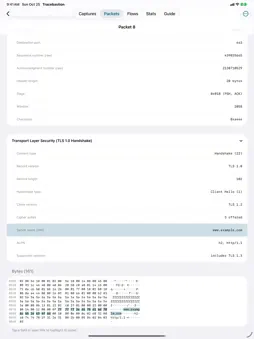
Tracebastion is a packet-capture analyzer for iPhone and iPad. Open .pcap and .pcapng files from Files, Mail, or AirDrop and inspect them entirely on device — a pocket workbench for reviewing captures you already have. OPEN ANY CAPTURE - Classic PCAP in both byte orders, with microsecond or nanosecond timestamps - PCAPNG with multiple sections and interfaces, enhanced and simple packet blocks - Ethernet with 802.1Q/QinQ VLAN tags, raw IP, BSD loopback, and Linux cooked captures DECODE EVERY LAYER - ARP, IPv4, IPv6 (with extension headers), TCP, UDP, ICMP, and ICMPv6 - DNS and mDNS queries and answers, including compressed names - TLS ClientHello server name (SNI) and ALPN, HTTP/1.x request and status lines - Packet detail with every decoded field linked to a highlighted hex dump FILTER LIKE A PRO - Wireshark-style display filters: ip.addr == 10.0.0.0/8 && tcp.port == 443, dns.qry.name contains "example", tcp.analysis.retransmission, proto == udp, frame.len > 1000 - and / or / not, parentheses, contains, regular expressions, and over 60 fields - Clear error messages, examples, and recent filters UNDERSTAND THE TRAFFIC - Conversations with per-direction packets and bytes, duration, TCP state, and handshake RTT - Endpoints with names learned from DNS answers in the capture (no lookups are made) - DNS transactions with response times and error codes - Protocol hierarchy, traffic-over-time chart, TLS server names, and HTTP hosts - Follow TCP and UDP streams as text or hex, with retransmitted bytes removed FINDINGS - TCP retransmissions, zero windows, resets, and unanswered connection attempts - DNS errors, ICMP unreachable messages, checksum and truncation notes - Cleartext exposure: unencrypted HTTP, Authorization headers sent without TLS, Telnet, FTP, POP3, IMAP, and SMTP - Tap any finding to filter the packets behind it EXPORT - Save filtered packets as a new .pcap (or .pcapng when link types are mixed) - CSV tables of packets, conversations, endpoints, and protocol hierarchy - PDF or text capture report with the file's SHA-256 fingerprint ONE PURCHASE, EVERYTHING INCLUDED - No subscription, in-app purchase, account, ads, analytics, or tracking - Captures are copied into the app and decoded on device; nothing is uploaded - A generated sample capture (documentation addresses only) lets you explore every screen before importing your own Tracebastion reads capture files; it does not capture live traffic or decrypt TLS. Analyze only captures you own or are authorized to inspect. Findings are header-based heuristics, not proof of compromise.
What's New
Version 2.0 2026-10-26
Tracebastion 2.0 is a complete rebuild around your own capture files. - Real PCAP and PCAPNG parsing (both byte orders, micro/nanosecond, multiple interfaces) ... Technical Analysis
Package Overview Basic metadata
Bundle ID
com.realbobcorbin.Tracebastion Current Version 2.0
Minimum iOS 17.0
Package Size App Store Size
Package Metadata 0 / 0 version records
Detailed binary, privacy manifest, framework, and Info.plist results have not been indexed for this package yet. The verified App Store and archive metadata above remains available.
Price History (USA store)
3 recorded price change points. These are historical observations, not a guarantee of the current price.
| Recorded at | Price | Currency |
|---|---|---|
| 2.99 | USD | |
| 0.0 | USD | |
| 3.99 | USD |
Developer Information
Known Version Records
0 version records with stored package metadata
Stored metadata does not guarantee a package is currently available to download.
| Details | Version / IDs | Version date | Action |
|---|